UN Regulation R151/R159/R158
View More

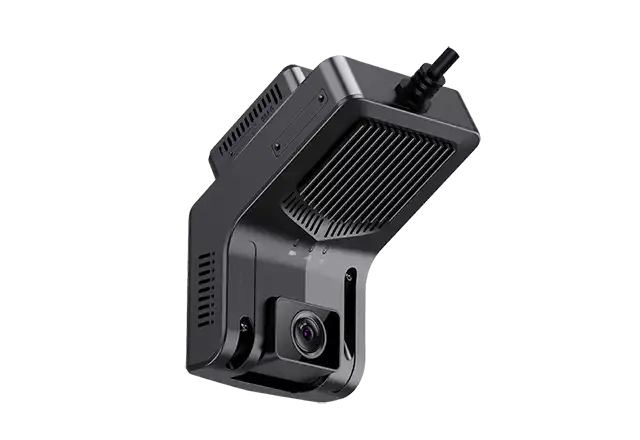
Fleet video is now central to collision investigation, driver coaching, claims management, and commercial vehicle safety. But cameras can also capture drivers, passengers, pedestrians, vehicle locations, and everyday behaviour. That makes privacy a serious operational issue. For European fleet operators, a GDPR-friendly fleet camera is increasingly important because better safety should not depend on uncontrolled surveillance. A GDPR-friendly fleet camera is not simply a dashcam with a privacy notice. It is a GDPR-friendly fleet camera, platform, and operating process designed around clear purposes, proportionate collection, controlled access, limited retention, and accountable data use.
A GDPR-friendly fleet camera matters because the GDPR is technology-neutral and applies to personal-data processing through technologies including video surveillance. The GDPR principles include lawfulness, fairness and transparency, purpose limitation, data minimisation, storage limitation, integrity and confidentiality, and accountability. It means GDPR-friendly fleet camera selection should consider more than resolution, night vision, storage, 4G, and AI. A GDPR-friendly fleet camera should also make privacy controls practical in daily fleet operations.
The term GDPR-friendly fleet camera should not be read as “automatically GDPR compliant.” Compliance depends on how a fleet decides why and how data is processed. The European Commission explains that the organisation determining the purposes and means of processing is the controller, while a processor acts on the controller’s behalf; processor responsibilities should be governed by a contract or other legal act. GDPR-friendly fleet camera is a solution designed to help fleets build a privacy-conscious workflow. A GDPR-friendly fleet camera should support configurable recording, clear retention controls, permission management, access logging, secure data handling, and controlled export or deletion.
Privacy by design and by default is particularly relevant. European Commission guidance says organisations should, by default, process only necessary data, use short storage periods, and limit accessibility. GDPR-friendly fleet camera therefore should not assume that every manager needs every camera channel or that every recording needs indefinite storage.
The strongest GDPR-friendly fleet camera strategy combines technology and policy. The GDPR-friendly fleet camera controls data flow. The fleet policy controls human behaviour. Together, they create an auditable system.
Before installing a GDPR-friendly fleet camera, define exactly why each camera is needed. “Employee monitoring” or “general surveillance” is too broad to guide a proportionate deployment. A more specific purpose might be collision investigation, review of defined high-risk driving events, vulnerable road user protection, or driver coaching after verified fatigue and distraction alerts.
Purpose limitation is a core GDPR principle. Organisations should identify specific purposes for processing and communicate those purposes to individuals; data should not simply be collected for undefined reasons.
GDPR-friendly fleet camera programme should therefore map each channel to a purpose. A GDPR-friendly fleet camera may use forward video to support collision evidence. The driver-facing camera may support defined fatigue or distraction events. A blind-spot camera may support pedestrian and cyclist safety. A rear camera may support reversing incidents.
This purpose map makes a GDPR-friendly fleet camera easier to govern. It also helps fleets challenge unnecessary functions. If the purpose is collision investigation, is continuous audio really necessary? If the purpose is driver coaching, does every manager need unrestricted live view?
A GDPR-friendly fleet camera should help the fleet answer one question repeatedly: does this data directly support the stated safety purpose?
More data does not automatically create more safety. A GDPR-friendly fleet camera should give fleets options to collect and upload only the data needed for a defined objective.
European Commission guidance states that personal data should be adequate, relevant, and limited to what is necessary. It also says organisations should assess how much data is needed and avoid irrelevant collection. Does the fleet need continuous cloud upload? Could local loop recording plus event-based upload achieve the same purpose? Is audio needed? Does the fleet need facial recognition, or would driver login be enough? Should every acceleration event trigger a video clip?
Event-based workflows can make a GDPR-friendly fleet camera more focused. For example, the GDPR-friendly fleet camera can maintain local loop recording while uploading clips only after a collision, harsh braking event, driver fatigue warning, or manual emergency trigger. Event-based upload is not automatically compliant, but it gives the controller more control over necessity and proportionality.
For B2B buyers, this is a useful procurement test. A GDPR-friendly fleet camera should offer granular configuration rather than forcing an “all cameras, all footage, all the time” model.
Driver-facing video often creates the most concern because it can capture a worker continuously inside the cab. A GDPR-friendly fleet camera should therefore support a more controlled approach to in-cab monitoring.
Start with the safety case. Is the GDPR-friendly fleet camera detecting fatigue, mobile phone use, smoking, seat-belt status, or distraction? Does the system send a short event clip after an alert, or can managers watch the driver live whenever they choose? Are AI events verified before coaching or disciplinary action?
A GDPR-friendly fleet camera should allow fleets to separate safety events from unrestricted observation. Role-based access, event-level permissions, restricted live view, configurable recording, and audit logs can all support a more proportionate workflow.
Worker monitoring can be intrusive. The UK ICO, in guidance relevant to UK GDPR rather than EU GDPR, says work-vehicle monitoring should be justified and notes that monitoring during private use will rarely be justifiable when private vehicle use is allowed.
Internally, the GDPR-friendly fleet camera should not be presented as a tool to “watch drivers.” The stronger message is that the GDPR-friendly fleet camera identifies defined safety events under documented access rules.
Keeping footage “just in case” can create unnecessary privacy exposure. A GDPR-friendly fleet camera should support short, defined retention periods and automatic deletion or overwrite.
European Commission guidance says personal data should be stored for the shortest time possible, taking account of the reason for processing and relevant legal obligations. Organisations should establish time limits for deletion or review. The retention period should follow purpose and context. Ordinary loop footage may have a short retention period. A collision clip may need to be preserved during an active insurance claim or legal investigation. AI coaching events may follow a separate review schedule.
A good GDPR-friendly fleet camera should support automatic overwrite, configurable retention, event locking, and controlled preservation of relevant evidence. This reduces reliance on manual deletion.
The fleet should also manage clips downloaded from a GDPR-friendly fleet camera. The GDPR-friendly fleet camera platform may automatically delete a video, but that control has limited value if managers have copied the footage into personal laptops, messaging groups, or uncontrolled shared folders.
A complete GDPR-friendly fleet camera policy controls footage from capture to final deletion.
A GDPR-friendly fleet camera should not give every user the same visibility. A safety director, depot manager, insurance specialist, and IT administrator have different responsibilities.
Role-based access is therefore a central GDPR-friendly fleet camera feature. Permissions can be separated by fleet, region, depot, vehicle group, camera channel, event type, and user role. An insurance team may need collision footage but not routine driver-facing events. An IT administrator may need device health information without viewing video.
European Commission privacy-by-default guidance specifically includes limited accessibility as part of default privacy protection. GDPR-friendly fleet camera should translate that principle into a simple default: users see only what they need.
Audit logs are equally valuable. A GDPR-friendly fleet camera should help authorised administrators determine who viewed, exported, downloaded, or deleted footage. This strengthens accountability and supports investigation of inappropriate access.
For multinational fleets, the GDPR-friendly fleet camera access model should also reflect geographic responsibilities. Using one GDPR-friendly fleet camera platform does not mean a manager in one country automatically needs driver video from every other market.
Fleet buyers often compare camera resolution, low-light performance, IP rating, operating temperature, storage, and AI. But a GDPR-friendly fleet camera is also a cloud and data-processing decision.
The fleet should understand where GDPR-friendly fleet camera video is stored, how it is transmitted, who can process it, which subprocessors are involved, and what happens when the customer terminates the service. The European Commission distinguishes controllers from processors and requires processor duties to be defined contractually. GDPR-friendly fleet camera provider should be able to discuss data-processing terms, security controls, deletion procedures, subprocessor governance, and data location. “Our cloud is secure” is not a sufficient enterprise answer.
International data transfers also need review. EU data protection rules provide mechanisms including adequacy decisions, Standard Contractual Clauses, and Binding Corporate Rules for relevant international transfers. GDPR-friendly fleet camera must always store data in a single EU country. It means the fleet should understand the data flow and apply appropriate safeguards.
For procurement teams, the cloud architecture should be evaluated as part of the GDPR-friendly fleet camera, not as a hidden technical detail after the cameras have been purchased.
7. Make Driver Transparency Part of the Rollout
Even a technically strong GDPR-friendly fleet camera can fail operationally when drivers do not understand what it does. Surprise creates resistance. Vague explanations create suspicion.
Before deployment, fleets should explain which cameras are installed, what data is collected, why the GDPR-friendly fleet camera is used, how relevant footage is retained, who may access it, and how individuals can exercise applicable data protection rights.
European Commission guidance describes rights including information, access, rectification, erasure in applicable circumstances, restriction, portability in relevant cases, and objection. GDPR-friendly fleet camera programme needs a practical request-handling process before the first request arrives.
Managers also need training. A GDPR-friendly fleet camera can have excellent permission controls but still be misused if an authorised user downloads a driver clip and shares it in a personal messaging group. GDPR-friendly fleet camera training should cover viewing, exporting, sharing, escalation, evidence preservation, and deletion.
Transparency is more than legal wording. In fleet safety, transparent deployment is change management. Drivers are more likely to accept a GDPR-friendly fleet camera when they understand the safety purpose and can see clear limits on management access.
A Data Protection Impact Assessment, or DPIA, should be considered early in a GDPR-friendly fleet camera project. European Commission guidance says a DPIA is required where processing is likely to result in high risk to individuals’ rights and freedoms, including large-scale systematic monitoring of public areas. A GDPR-friendly fleet camera programme should bring data protection, legal, fleet safety, IT, and procurement stakeholders into the design stage.
For a GDPR-friendly fleet camera, a DPIA can help describe processing, examine necessity and proportionality, identify risks, and define safeguards. The EDPB also identifies large-scale systematic monitoring of publicly accessible areas as an important DPIA scenario.
GDPR-friendly fleet camera vendor can support the assessment by providing data-flow diagrams, cloud architecture, retention controls, camera functionality, AI descriptions, permission models, and security information. However, the customer should not assume the vendor can make the controller’s legal decision.
Early privacy review can make a GDPR-friendly fleet camera easier to standardise across vehicle types, branches, and European markets.
AI is changing how a GDPR-friendly fleet camera is deployed in the fleet video market. A GDPR-friendly fleet camera may detect fatigue, distraction, mobile phone use, forward collision risk, lane departure, pedestrians, cyclists, and other defined events.
The strongest use of AI is focus. Instead of asking safety teams to watch hours of video, a GDPR-friendly fleet camera can surface relevant clips for authorised review. That can make driver coaching more timely and incident investigation more efficient.
However, AI does not remove data protection responsibilities. A GDPR-friendly fleet camera using AI still needs a defined purpose, proportionate data collection, retention rules, access controls, security, and human governance.
Fleets should ask how AI outputs are used. Does an alert trigger coaching, or automatic punishment? Are false positives reviewed? Can the driver challenge an event? Is human verification required before a significant decision?
GDPR includes protections relating to certain solely automated decisions with legal or similarly significant effects. GDPR-friendly fleet camera should therefore support human review where the fleet’s use of AI may materially affect an individual.
The better B2B message is not “the GDPR-friendly fleet camera watches everything.” It is “the GDPR-friendly fleet camera helps authorised safety teams find defined events faster under controlled rules.”
Fleet video may contain faces, vehicle registration information, locations, customer premises, road incidents, and driver behaviour. A GDPR-friendly fleet camera should therefore be evaluated as a connected data system.
Security questions should cover device credentials, communications, platform authentication, user permissions, audit logs, software updates, vulnerability handling, account removal, and cloud security. The GDPR-friendly fleet camera should fit into the fleet’s broader IT and cybersecurity controls.
The supplier should also have an incident process. European Commission guidance says that when a personal data breach is likely to pose a risk to individuals’ rights and freedoms, the supervisory authority must be notified without undue delay and, at the latest, within 72 hours after the organisation becomes aware of the breach. A GDPR-friendly fleet camera programme also needs authorised personnel, internal procedures, manager training, regular account review, and clear escalation paths.
For GDPR-friendly fleet camera procurement, privacy and cybersecurity should sit alongside 1080P or 2K resolution, night vision, WDR, 4G, Wi-Fi, GPS, storage, AI accuracy, and vehicle-grade durability. The GDPR-friendly fleet camera is part of the fleet’s data infrastructure.
When comparing vendors, ask the following questions.
A GDPR-friendly fleet camera should make responsible governance operationally achievable. Privacy cannot depend on a fleet manager remembering dozens of manual steps every day.
The fleet safety market sometimes presents privacy and video evidence as opposing goals. They do not have to be. A well-designed GDPR-friendly fleet camera can collect video for defined safety purposes while reducing unnecessary collection, access, retention, and sharing.
Privacy controls can also improve operations. Event-based upload can reduce the footage safety teams review. Role-based access can reduce internal confusion. Shorter retention can reduce unnecessary storage. Audit trails can strengthen accountability. Clear driver communication can improve adoption. In this sense, a GDPR-friendly fleet camera turns privacy principles into a disciplined fleet video process.
The key is to treat data protection as a system-design requirement rather than a final legal checkbox. Select the GDPR-friendly fleet camera with privacy controls in mind. Define purposes before activation. Minimise data. Set retention rules. Restrict access. Understand cloud flows. Review AI workflows. Train managers and drivers.
For OEMs, logistics companies, bus operators, construction fleets, public-service fleets, and other commercial vehicle organisations, the next generation of video safety should be safer, smarter, and more accountable. A GDPR-friendly fleet camera is not about recording less at any cost. It is about collecting and using the right data for the right safety purpose with the right controls.
When fleet safety and privacy are designed together, the GDPR-friendly fleet camera becomes more than a compliance feature. The GDPR-friendly fleet camera can become a stronger foundation for trusted driver coaching, faster incident investigation, scalable fleet management, and responsible AI-enabled vehicle safety.